A Valid Login Can Still Be an Attack. What Happens Next?
 Aislan Foina: Oct 19, 2026
Detect Suspicious Activity. Contain the Threat Precisely. Establish What Was Affected and How Quickly Access Changes Reach AI.


Panzura
Our enterprise data success framework allows enterprises to build extraordinary hybrid cloud file and data systems.

Platforms
Complementary file and data platforms that deliver complete visibility, control, resilience, and immediacy to organizations worldwide.

Solutions
From data resilience to global file delivery, we solve the toughest and most important data problems facing organizations globally.

Resources
Find insights, news, whitepapers, webinars, and solutions in our resource center.

Company
We bring command and control, resiliency, and immediacy to the world’s unstructured data. We make it visible, safeguard it against damage, and deliver it instantly to people, workloads, and processes, no matter where they are.
13 min read
Table of Contents
Detect Suspicious Activity. Contain the Threat Precisely. Establish What Was Affected and How Quickly Access Changes Reach AI.
Key Takeaways:
The login is real. The person using it isn’t.
Compromised identity is now a leading route into ransomware incidents. In the Sophos State of Ransomware 2026 survey of 2,158 organizations hit in the past year, 79% of attacks started with compromised identities. Malicious email (26%) and phishing (24%) were the leading root causes, ahead of exploited vulnerabilities for the first time in the last four years of the report.
Once inside, the attacker may initially look like an authorized user. The session is valid, the permissions are legitimate, and the file protocol is the one your people use every day. Authentication has succeeded. That does not establish whether the activity that follows is safe.
Harmful activity does not always require stolen credentials, either. A departing employee copying client folders or sensitive data, a contractor deleting the wrong project, or a script that renames ten thousand files can operate through legitimate permissions. The account is authorized, yet the outcome may not be intended.
The first post in this Cybersecurity Awareness Month series asked how much work your company would redo after an incident. This one asks another question: How much damage can occur before suspicious activity is detected and effectively contained, and how much legitimate work does that response interrupt?
It applies to the people using your file data, and increasingly to the AI assistants and agents working from the same files through connected retrieval tools.
The answer requires a connected workflow that recognizes suspicious behavior, stops further damage, establishes what was affected, and carries access changes through to the systems that retrieve the data.
Identity, endpoint, network, and email defenses remain essential. A valid login can pass an authentication check, but suspicious behavior can still be detected elsewhere. The file platform contributes another vantage point, which is the operations performed against shared data.
Shared file storage can create detection blind spots. Researchers at La Trobe University, according to an article in HelpNet Security, found that ransomware encrypting files on a remote file server is hard for endpoint agents to catch, because the server-side agent sees ordinary file-serving activity while the client-side agent sees only an application touching a mapped drive. Their conclusion was that detection should reside where the file operations happen.
Known-threat signatures can contribute useful evidence. But the evaluation should not stop at whether a platform recognizes a known ransomware family. Ask how it identifies suspicious activity when the tool, account, or attack sequence has not been seen before.
The cost of slow detection is no longer only encryption. In the Sophos survey, 56% of attacks encrypted data, and 16% both encrypted and stole it. Recovery restores files. It does not retrieve those already copied and exfiltrated.
That makes the interval between suspicious activity and effective containment a business issue. Measure what happens during that interval including files changed, data read, users affected, and work interrupted.
Image 1. Five mechanisms for defense in depth with Panzura CloudFS
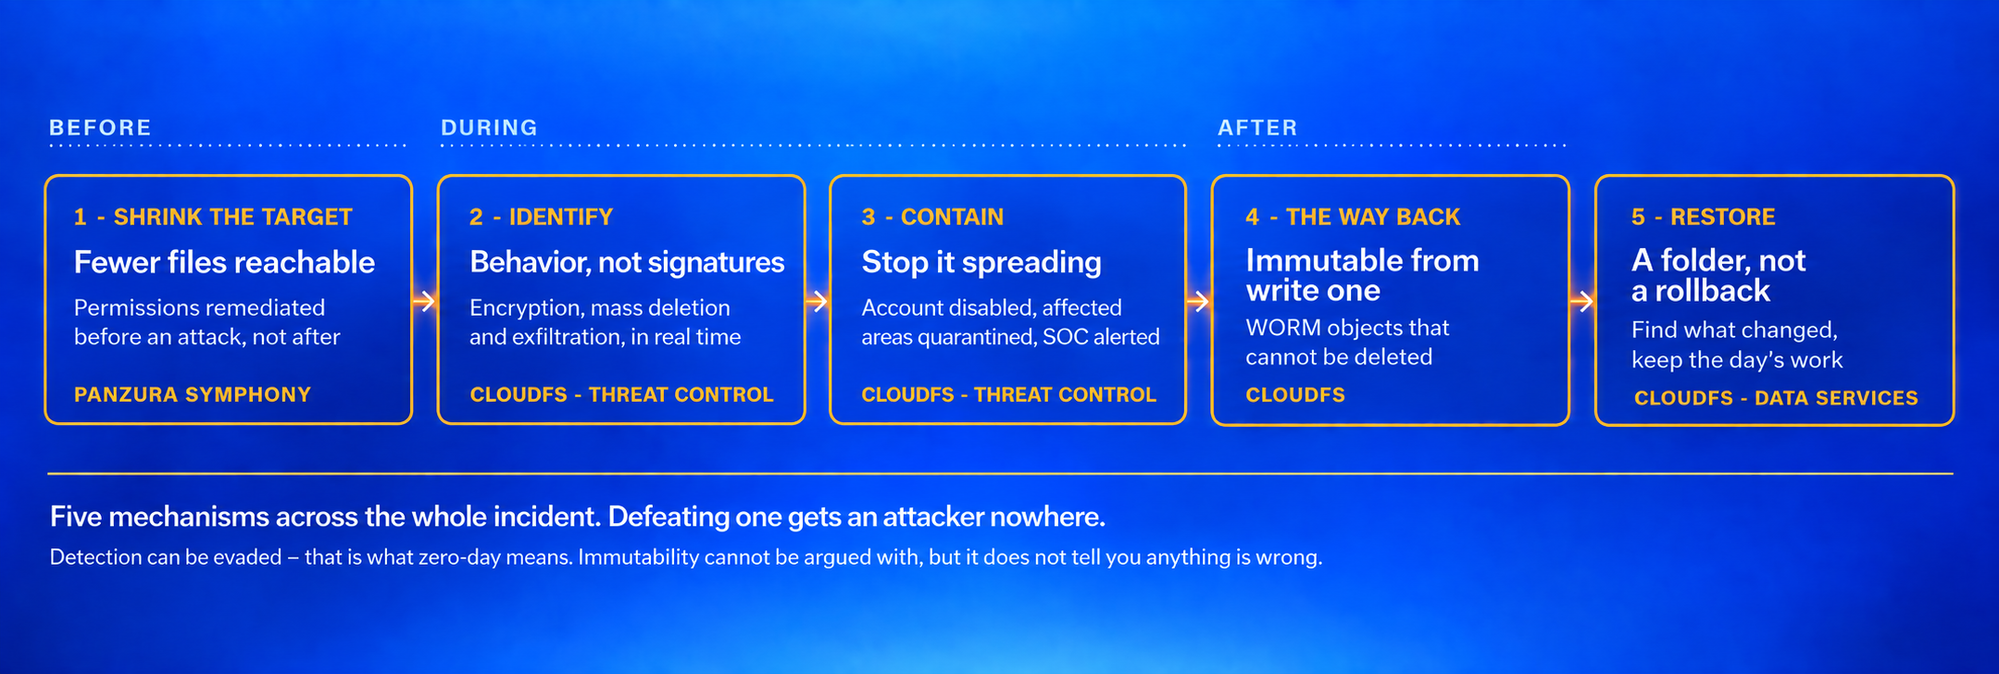
When an account has legitimate access, its behavior provides important context. Is this activity normal for this user? Is the volume unusual? Does the pattern suggest encryption, destructive changes, or potential data theft?
Panzura CloudFS uses AI-powered behavioral analysis to build user profiles from activity in your own environment. It looks for anomalies associated with ransomware, data destruction, and potential exfiltration including unusual file changes, access patterns, and copying activity. The aim is to recognize suspicious behavior rather than simply match known ransomware signatures.
The architecture combines cloud-based analysis of file activity metadata with targeted local file-content inspection when deeper analysis is needed. The behavioral profiling runs in The CloudFS SaaS environment on audit events alone, so there is no new server to deploy and no added processing load on the customer’s own systems, and file content is never sent out of the environment. When suspicious activity warrants a closer look, the content inspection happens inside the CloudFS node itself. That distinction matters. Metadata analysis and content inspection are different processing steps. Ask what information is processed, where it is processed, and which connections the service requires.
Remember that many vendors in this space claim “behavioral detection,” but that does not establish how a platform will perform in your environment. Ask what creates the baseline, which operations it observes, and how it distinguishes suspicious activity from legitimate high-volume work. An overnight processing job, an authorized migration, and a destructive script should all be part of the evaluation, not just a ransomware simulation.
Coverage also needs a more precise answer than a list of supported storage protocols. Some platforms document ransomware monitoring for SMB but not NFS or FTP. Detection, audit, access control, and containment are separate capabilities. Establish each of these capabilities for every access path you use.
Table 1. Detection capabilities compared
Identifying an attack is the first job. An alert alone does not stop the next file operation. What decides the cost of the incident is how quickly it stops spreading, and how much of the business stops with it.
Panzura CloudFS delivers the ability to disable compromised accounts and quarantining affected areas. That connects detection to action rather than leaving every response dependent on someone reading an alert.
The next question is how precisely that action is enforced. Ask which identity, session, address, or resource is blocked, whether existing sessions remain usable, and how quickly the response reaches other sites and supported access paths. Measure whether unaffected users can continue working rather than assuming they can.
Containment also varies by protocol on some platforms. Public documentation of vendors in this category includes examples of automated mitigation limited to SMB even where detection supports additional protocols. It also includes configurations in which blocking a shared access-server address can interrupt other users or applications. A successful block is not necessarily a precise block.
Evidence matters alongside the response. CloudFS provides file activity auditing and investigation capabilities. Establish which events your configuration captures, how they reach your security tools, and whether responders can connect the detection, containment action, and affected files in one investigation.
Table 2. Containment and evidence capabilities compared
Also test the exception path. If legitimate activity triggers containment, who can review the evidence, restore access, and prevent an unnecessary repeat? The response workflow should be operationally useful on an ordinary working day, not only during a staged attack.
Once the account is stopped, the next question is what damage may have been done. The answer decides the scope of recovery.
CloudFS brings global search and file activity auditing to the investigation. Responders can search across the managed file estate and examine activity to help establish what changed, which identity performed the operations, and when they occurred. That evidence helps narrow the recovery scope before a restore begins.
CloudFS delivers the fastest global recovery capabilities, with a recovery point objective (RPO) of 60 seconds, among all evaluated vendors in a recent Frost & Sullivan Radar™, providing unmatched business continuity across all sites. This industry-best recovery speed is achieved through a distributed protocol that ensures transactional integrity across the entire system, enabling organizations to maintain operations during active security incidents at any location.
CloudFS also supports the incident report and subsequent investigation. When evaluating competitive solutions, be precise about unusual read or copy activity and if it can indicate potential exfiltration. That does not by itself prove where the data went. Detection should flag suspicious activity, limit further access, and the audit record should help responders investigate the preceding activity.
The mechanics of restoring a file or folder were the subject of the first post in this series. Here, the critical connection is between investigation and recovery. That is, identifying the affected set, selecting an appropriate recovery point, and validating the restored data before returning it to use. A fast restore is not the same as a trusted restore.
Table 3. Incident scenarios to test in evaluation
Detection confidence is knowing, before an incident, what the platform will recognize, how fast it will act, who else will be affected, and what the record will show afterward. It depends on more than the file platform. Identity security, endpoint protection, and incident response remain essential. What the file platform adds is direct visibility into activity against the shared files it manages.
Analysts have begun to treat that as a category. Panzura is a Representative Vendor in the 2026 Gartner® Market Guide for Cyberstorage, and we believe the report reflects a broader shift toward active defense and AI-powered threat detection built into the storage layer itself.
The 2026 Gartner Market Guide for Hybrid Cloud Storage also recognizes Panzura, and in our view the integrated threat detection in CloudFS is part of why. Frost & Sullivan cited real-time threat detection among the technical advantages of CloudFS in its Frost Radar for hybrid cloud storage, and the Globee® Awards for Technology named CloudFS Best of Category for ransomware protection.
The stronger evidence, however, is an observed result. How much damage occurred before containment, how much legitimate work was interrupted, how quickly responders established the affected-file set, and whether they could trust the recovery.
Ask for the complete configuration behind that result, including software versions, required services, licensing, network conditions, and response settings. A feature available somewhere in a product portfolio is not the same as a capability configured and operating in your deployment.
A stolen account is about more than file shares. If your organization uses Microsoft 365 Copilot, that account may also be able to retrieve connected file content through AI. That creates another access path to consider during containment.
Two questions matter. Which permissions govern the answer, and how quickly do permission changes reach the retrieval system? Permission-aware search is necessary, but an outdated permission record can still create an exposure window.
Panzura Nexus makes CloudFS file content available to Microsoft 365 Copilot without migrating the source files into a separate data lake. Existing NTFS permissions map to Microsoft Entra ID, and Copilot enforces the resulting access permissions at query time. An event-driven pipeline propagates file and permission changes. With Panzura Nexus, those updates occur within seconds. The approach preserves the existing file-permission model rather than requiring administrators to recreate it as a separate AI access policy.
When evaluating competing solutions, test that sequence end to end. Change a user’s file permissions and measure when subsequent Copilot retrieval stops returning the restricted content. Separately establish how a security-driven account block affects AI access. Do not assume every containment action changes the permissions or identity state used by Copilot. The objective is to stop subsequent unauthorized retrieval.
Agentic AI raises the bar again. An agent should operate under a defined identity, use only authorized content, and leave a record of what it did. CloudFS and Panzura Nexus provide the governed file foundation. The agent’s own identity model, tool permissions, and audit controls still need to be validated with the AI platform in use.
A ransomware-detection claim is the beginning of an evaluation, not its conclusion. These questions connect the claim to an operational result. Put them to every vendor on your list, including us.
In a controlled, nonproduction environment, give a test account normal permissions and simulate encryption, destructive changes, and unusual copying. Run authorized high-volume activity alongside those tests. Include the sites and access paths your organization actually uses.
Single-site firms can ask the same questions. Panzura Express is CloudFS for one location, with AI-powered cyber resilience and Panzura Nexus included.
Learn more about Cyber Resilience with Panzura. Next in this Cyber Resilience blog series we explore what your AI can reach and its implications. The series ends with a live webinar, “Three Questions to Ask Every File Platform About Cyber Resilience in the AI Era,” with Darrin Chapman and Raul Sanchez.
Frequently Asked Questions (FAQs)
Yes. Panzura Express is the single-site edition of Panzura CloudFS, delivered as software with no hardware to procure. It bundles CloudFS with a high-availability node pair, Panzura Data Services and Panzura Nexus in one annual license, available in three capacity tiers, and is sold and deployed through Panzura channel partners. The detection, containment, investigation and recovery questions in this article apply unchanged: the same behavioral analysis, the same 60-second write interval to immutable object storage and the same permission-preserving path to Microsoft 365 Copilot. The difference is scope. Express is sized and priced for one location, and partners handle deployment, so a mid-market firm does not have to assemble file storage, cyber resilience and AI readiness from separate products.
No. Behavioral profiling runs in Panzura CloudFS’s SaaS environment on audit events from your CloudFS deployment, so there is no additional server to deploy, no agent fleet to maintain and no added processing load on your own systems. File content is not sent out of your environment for analysis. When suspicious activity warrants deeper inspection, the content check runs inside the CloudFS node itself. Ask every vendor the same three questions: what information leaves the environment, where it is processed and what connectivity the service requires. Several platforms in this category require additional components or external feeds, and the answer affects both your security posture and your deployment timeline.
Behavioral threat detection and response is a licensed capability. It runs on the Panzura CloudFS estate you already have, so there is no separate appliance, parallel index or second console to deploy. What CloudFS carries by architecture at every site is the foundation detection builds on: global file locking, data written to object storage every 60 seconds as new immutable objects, snapshots with policy-set retention and recovery to a clean point in time. Those are not add-ons or premium tiers. When comparing vendors, ask for the complete configuration behind any demonstrated result, including software versions, required services, licensing and response settings. A capability available somewhere in a portfolio is not the same as one operating in your deployment.
Run it, in a controlled nonproduction environment, with your own access paths and sites. Give a test account normal permissions and simulate encryption, destructive changes and unusual copying. Alongside those tests, run authorized high-volume work: an overnight job, a migration, a service account script. A platform that catches the simulated attack but also stops legitimate bulk activity will cost you working days. Record detection time, containment time, files changed before containment, and the effect on other users and sites. Then test the exception path: who reviews the evidence, restores access and prevents a repeat false positive. Panzura’s evaluation checklist of twelve questions is designed for this; put it to every vendor on your list, including Panzura.
Panzura CloudFS provides global search across the managed file estate and file activity auditing, so responders can establish what changed, which identity performed the operations and when. That evidence narrows the recovery scope before any restore begins, which matters because restoring more than necessary interrupts work that was never affected. With changed data written to object storage every 60 seconds as new immutable objects and snapshot recovery points on a configurable schedule, you can select a point in time close to the incident and validate the restored data before returning it to use. Confirm which events your configuration captures and how they reach your SIEM or other security tools so the investigation and the incident report draw on the same record.
Only what its current permissions allow, and only for as long as those permissions stand. Panzura Nexus makes Panzura CloudFS file content available to Microsoft 365 Copilot without moving files into a separate data store. Existing NTFS permissions map to Microsoft Entra ID, and Copilot enforces them at query time. Changes to files and permissions propagate through an event-driven pipeline within seconds, so a revoked permission closes the AI access path quickly rather than after a nightly refresh. In your evaluation, change a user’s file permissions and measure when Copilot stops returning the restricted content, then separately confirm how a security-driven account block affects AI access. Do not assume every containment action reaches the identity state Copilot uses.
Yes. Panzura Express is the single-site edition of Panzura CloudFS, delivered as software with no hardware to procure. It bundles CloudFS with a high-availability node pair, Panzura Data Services and Panzura Nexus in one annual license, available in three capacity tiers, and is sold and deployed through Panzura channel partners. The detection, containment, investigation and recovery questions in this article apply unchanged: the same behavioral analysis, the same 60-second write interval to immutable object storage and the same permission-preserving path to Microsoft 365 Copilot. The difference is scope. Panzura Express is sized and priced for one location, and partners handle deployment, so a mid-market firm does not have to assemble file storage, cyber resilience and AI readiness from separate products.

Aislan Foina is Director of Software Development at Panzura. He has published several academic papers and patents. Aislan holds an electronic engineer degree and a Master's in Microelectronic from University of São Paulo, PhD in Pervasive Computing from Barcelona Supercomputing Center, and has been a software developer since 1991. He is fluent in English, ...
Aislan Foina: Oct 19, 2026
Detect Suspicious Activity. Contain the Threat Precisely. Establish What Was Affected and How Quickly Access Changes Reach AI.
 Darrin Chapman: Oct 16, 2026
How Much Legitimate Work Survives, How Narrowly You Can Restore, and Whether Microsoft 365 Copilot Sees the Restored Files
 Karthik Ramamurthy: Sep 10, 2026
Authority Decides Whether an Agent May Write Yet It Says Nothing About What Happens When Two of Them Do