Skip to the main content.
Panzura-Icon-FullColor-RGB@0.75x

Panzura

Our enterprise data success framework allows enterprises to build extraordinary hybrid cloud file and data systems.

architecture-icon

Platforms

Complementary file and data platforms that deliver complete visibility, control, resilience, and immediacy to organizations worldwide.

Layer_1-1

Resources

Find insights, news, whitepapers, webinars, and solutions in our resource center.

Layer_1-2

Company

We bring command and control, resiliency, and immediacy to the world’s unstructured data. We make it visible, safeguard it against damage, and deliver it instantly to people, workloads, and processes, no matter where they are.

Data Sovereignty & Compliance

Know what you hold. Control where it goes. Prove it when someone asks.

Auditors do not ask one question. They ask what sensitive data you hold, where it is allowed to go, who may reach it, how long you keep it, and what you can evidence — each with a deadline attached, and usually about files nobody has opened in years.

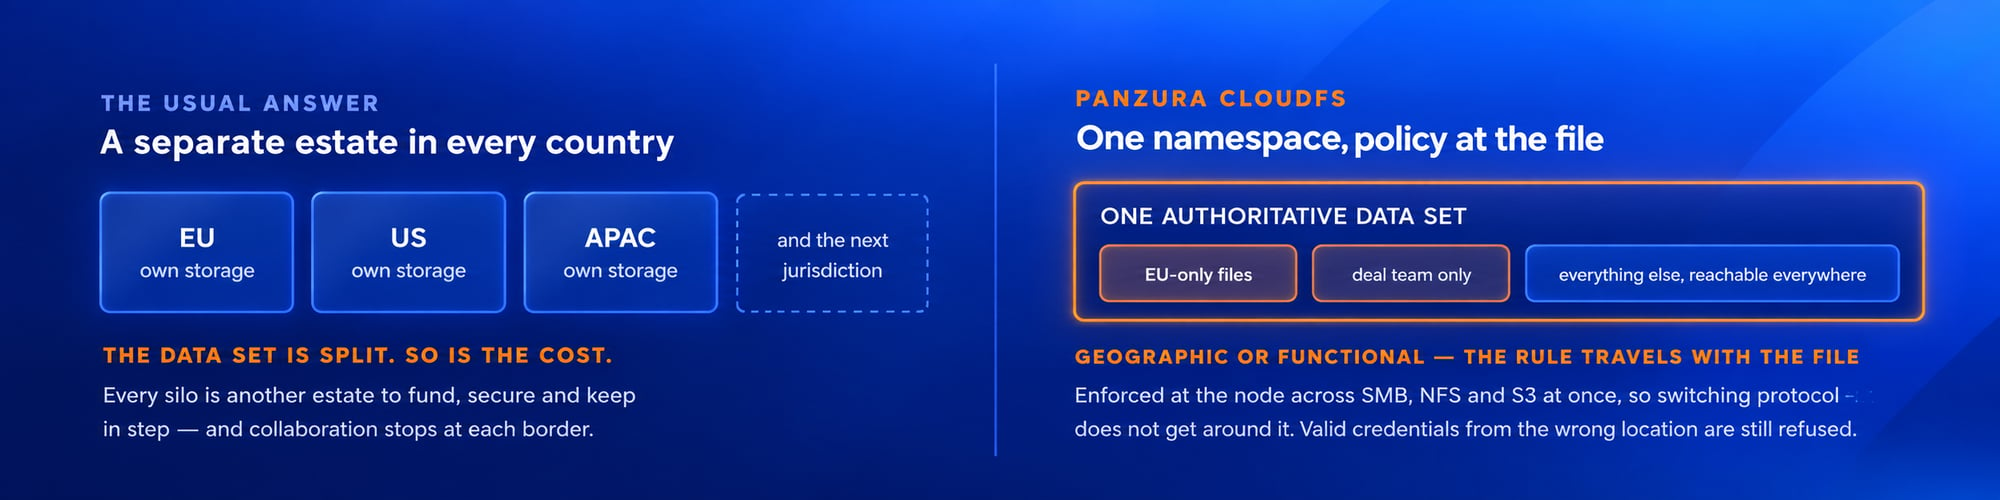
Panzura Symphony scans and tags what you hold. Panzura CloudFS enforces the access boundary, applied at the node across SMB, NFS and S3 at once, so switching protocol does not get around it. The boundary can be a jurisdiction — or a department, a deal team, a client.

Sensitive data found and classified automatically · Retention and legal hold enforced by policy · File-level boundaries, geographic or functional · One audit record across every site · Panzura Nexus governs AI access to the same data.

ChatGPT Image Sep 17, 2026, 04_57_27 PM
How to evaluate it

 What jurisdictional controls must do to work.

All competitors in this category claim compliance support. What separates them is where the rule resides, whether it holds true on every route to the data, and whether you can prove it held. It comes down to whether there is one truth, whether enforcement is always live, and whether it reaches everywhere. Ask the following question of us, then ask everyone else.
use-case-sov-1
One Truth
What's the impact on your infrastructure?

The standard answer to residency is a storage instance per region. It works, and it fragments the estate — teams in one jurisdiction cannot collaborate with teams in another, deduplication happens per silo rather than globally, and every additional regime adds another thing to fund and secure. Ask what the architecture requires, not what the policy screen offers. Panzura CloudFS delivers:

  • One source of truth across every site and cloud
  • One authoritative data set with geographic policy applied per file, folder or pattern
  • No duplicate regional deployments
  • Supports compliance requirements when data must reside in a named region
collab1-1
Always Live
What happens when the rule changes?

Regulations move, projects get reclassified, and a jurisdiction is added because the business won work there. If enforcement depends on where data was placed, changing the rule means moving data. Ask how long a policy change takes to take effect, and what has to happen physically for it to hold. Panzura CloudFS delivers:

  • Policy enforcement applies instantly at the site level — a rule change is a rule change, not a migration
  • Rules match on patterns, so new files falling inside a classification are covered without anyone tagging them
  • When data does need to move, Panzura Symphony orchestrates it at petabyte scale
use-case-sov-2
Everywhere
Can somebody route around it?

Ask whether the same rule holds over SMB, NFS and object access, what happens when an AI pipeline reads the data, and whether a user with legitimate credentials in the wrong country is stopped or merely logged.

  • CloudFS — enforced at the node across SMB, NFS and S3 simultaneously, and applied irrespective of file system or Active Directory permissions
  • CloudFS — adds the "where" dimension to authentication: valid credentials from an unauthorized location are refused
  • Panzura Data Services — the audit record that shows the rule held, on every path
  • Panzura Nexus — AI retrieval governed by the same file permissions, so a prompt cannot reach what the user could not
How geofencing works

The rule travels with the file, not the box.

Geofencing in Panzura CloudFS identifies files, folders or patterns and restricts access based on the geographic location of the site requesting it. Enforcement happens at the node and applies to reads and writes regardless of a user's file system or directory permissions, which is what makes it a boundary rather than a preference.

To be precise, geofencing governs who can reach a file and from where. The physical storage location of files are a separate control, handled by placing data in named cloud regions. The two are often discussed simultaneously but they address different questions.

The boundary does not have to be a geographic border. The same mechanism ring-fences by function — a department, a project, a deal team, a client. So, it's not just about regulatory compliance. It's also about the business case. Compliance and consolidation are usually presented as a trade off. File-level policy is what removes that trade off.

📄 Article | 7 min read | Enforcing Data Residency and Compliance with Panzura CloudFS Geofencing Policies

📄 Press release | 8 min read | Panzura CloudFS Tackles the $3.1 Trillion Data Silo Problem with Geofencing and Native S3 Interface

ChatGPT Image Sep 23, 2026, 08_19_13 PM
use-case-sov-3-1
Client Confidentiality
Walls that hold without separate infrastructure.

Professional services firms working for competing clients need genuine separation and usually build it out of folder permissions plus trust. A protocol-layer boundary holds even where directory permissions would have allowed access, and it does not require a second estate per client.
use-case-sov-4
Deal Teams & Projects
Ring-fence a team, then release it.

An M&A workstream, a bid team, a sensitive investigation. Scope a boundary around the files and the sites that should hold it, and remove it when the work concludes — a policy change rather than a data move.
use-case-sov-5
Commercial & controlled work
Both workstreams, on one file estate.

Firms running sensitive programs alongside commercial projects have historically segregated the whole estate to protect a fraction of it. Functional and geographic boundaries can be applied to the files that need them and nothing else.

Panzura CloudFS Compliance Support

Different rules, one enforcement point with CloudFS.

Most organizations are not managing one regulation. They are managing several at once, across offices that each answer to different authorities, on projects that cross borders by design.
ai1-1
GDPR and data residency
EU data that has to stay in the EU.

Geographic restriction applied at the file rather than the storage tier, so a single global namespace can hold regulated and unregulated data without a separate estate for each. Audit trails record who accessed what, when, and from where.
collab1-4
ITAR and Sensitive Work
Controlled files, on shared infrastructure.

Firms running commercial and government projects side by side can keep ITAR-regulated files inside authorized boundaries without segregating the whole estate, and without relying on users to remember which share is which.
blog62
FIPS 140-3 Certified
Encryption, boundary, and evidence together.

FIPS 140-3 certified encryption at rest and in transit, protocol-layer boundary enforcement, and an immutable audit record — the three things an assessor asks for separately. Panzura partners with OneTier on accelerating CMMC 2.0 readiness.
ChatGPT Image Aug 25, 2026, 02_09_12 PM

Where sovereignty is the requirement.

Residency and sovereignty get used interchangeably and they are not the same obligation. Residency is where data sits. Sovereignty is whose law it answers to, which turns on where it is stored, who holds the keys, and whether a foreign authority can compel disclosure. Data in a US provider's European region can still be reached under the CLOUD Act, which is why residency alone does not settle it.

CloudFS is built so that none of those three depends on us. The authoritative data set can sit in on-premises or in-country object storage rather than a hyperscaler region — CloudFS runs on bare metal and the common hypervisors, and writes to S3-compatible stores including on-premises platforms. Encryption keys are generated, supplied and controlled by the customer, with the private key held at your premises rather than in the cloud, and key management integrates with your own KMIP server.

For installations that cannot have any external communication at all, CloudFS has long offered a private secure site mode that disables outside communication entirely — no external IP addresses, no outside monitoring path.

Before the Clock Runs Out

Prove what happened, when it happened.

Regulated data raises the same question twice: once when an auditor, a court, or a data subject asks what happened to a file, and again when something goes wrong and the law sets a clock on your answer. Both demand the same thing, a complete and trustworthy record of every file, every access, and every change, across every site. Panzura keeps that record as the data is written, not reconstructed afterward, so the evidence is ready,

Prove it on demand

The question always arrives with a deadline.

A subject access request, a discovery order, an audit finding — each is the same problem: locate every instance, show who touched it, and evidence that the controls held. Ask for file-level audit detail rather than summary reporting, because in this market the honest answer is often summary.

  • Panzura Data Services — estate-wide search and file activity audit, one record across every site

  • Panzura Data Services — audit events streamed to your SIEM and compliance platform from a single feed

  • Panzura CloudFS — immutable version history, so the evidence is as tamper-resistant as the data

  • Panzura Symphony — exportable reports and support for Grafana dashboards

Report accurately when it goes wrong

A breach of notification is a factual claim with a timeline.

GDPR gives you 72 hours. Most regimes now require you to say what was accessed, not merely that something happened — and the penalty for guessing wrong runs in both directions, since over-reporting damages you and under-reporting is a second violation.

  • Threat Control for CloudFS — behavioral fingerprint per user, flagging encryption, mass deletion and exfiltration as they occur

  • Threat Control for CloudFS — incident evidence logged as the event unfolds, not reconstructed afterward

  • Panzura Data Services — file activity audit showing which files were reached, by which account, and when

The AI part of compliance

Where the data may go is one question. Who may reach it is another.

AI deployment is itself becoming a regulated surface, and an assistant pointed at the file estate is a new route to regulated data. Panzura Nexus enforces the existing file permissions on every query rather than maintaining a separate AI access policy, so adopting AI does not create a second control plane to govern, audit and defend. What a user cannot read, AI cannot retrieve.

panzura-nexus
Start where you are

Test the boundary before you have to defend it.

Compliance claims get examined at the worst possible moment. Talk to Panzura about the compliance mandates you must support. We will look at where your regulated data resides today, what it costs to keep it separate, and what a file-level boundary would replace.
nas3-1
If you already run CloudFS
Geofencing arrived in 8.6.

If you are on an earlier release, file-level geographic policy is an upgrade rather than a purchase. Later releases added audit streaming to several platforms at once, so your SIEM and your compliance tooling can take the same feed.

  • Check your release
  • Write one policy against one regulated project
  • Verify it holds over SMB, NFS and S3
ai3-3
If you face audits
Get insights and intelligence for CloudFS.

Panzura Data Services ensures you can see it, operate it, and trust it. Transform your Panzura CloudFS fo;e data into a transparent, auditable, and actionable data estate with visibility, governance, and real-time metadata intelligence

  • PDS Essentials with every CloudFS deployment; delivers centralized visibility, real-time monitoring, and custom alerting.
  • PDS Standard extends these capabilities with enterprise-class search, comprehensive audit trails, and one-click file recovery
828bde65-841a-453b-ba0b-c660ef7d126f
If you are a single site
Panzura Express, through a Panzura partner.

Small organizations often have the same regulatory compliance obligations as large firms. Panzura Express is CloudFS for a single site with a local high-availability node pair, Panzura Data Services and Panzura Nexus included, delivered by a Panzura partner.

  • Talk to a Panzura partner; we'll help you find one if you don't know where to start
  • When you're ready, add new locations later without re-platforming